







CySA+ and Security+ certified blue-team defender. I build my own SOC, then break it, investigate it, and harden it. Every step is documented in public. Open to SOC Analyst and Detection Engineering roles — NYC or remote.
|
Two ESP32-C5 boards run custom promiscuous-mode firmware and stream 802.11 frame metadata over UART into a stdlib-only FastAPI detection engine (deauth flood, evil twin, beacon/probe flood and RSSI anomaly rules), which forwards scored threats to Wazuh over RFC 5424 and drives a Next.js SOC console. Sensor to SIEM to analyst view, every layer mine. Two of the four detections map to ATT&CK: T1557 (evil twin) and T1499 (deauth flood). Run against my own network only, on hardware I own. The sensor forwards threats and summaries, never raw frames: the SIEM stores decisions, not a packet archive.
|
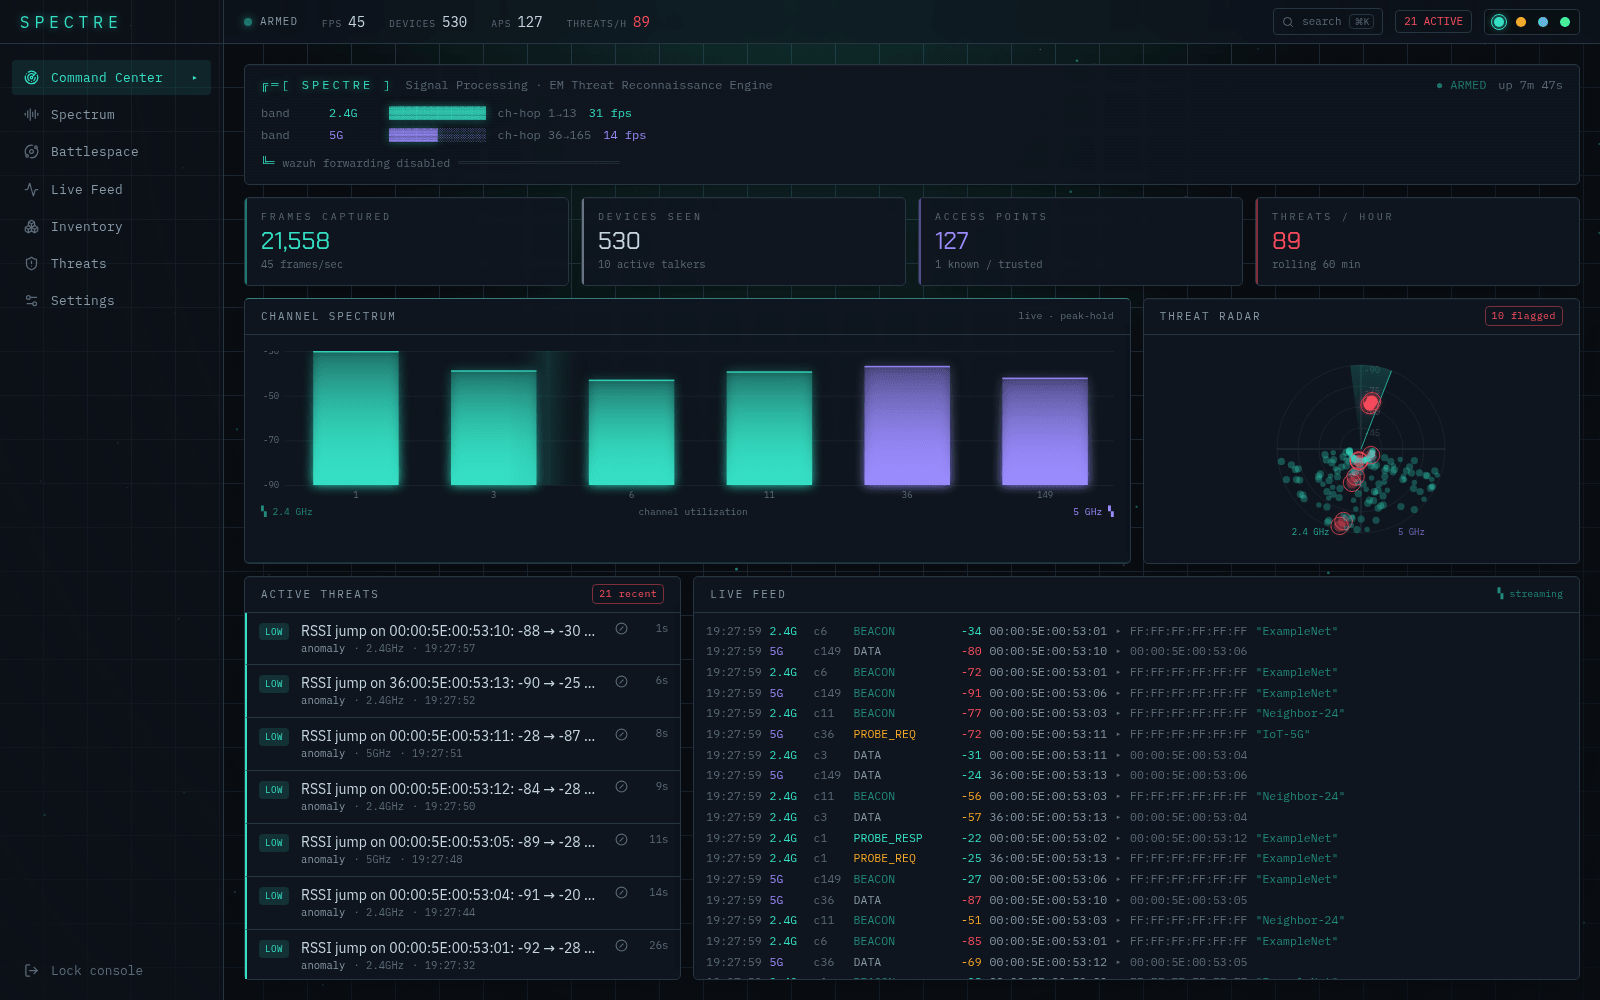
|


SPECTRE is one source among several. Everything lands in a self-built SOC running on a single Proxmox node behind a pfSense perimeter, five VLAN segments, default-deny between them.
flowchart LR
EP["Linux / Windows hosts<br/><i>Wazuh agents · FIM · auditd · SCA</i>"] --> SIEM
FWL["pfSense<br/><i>firewall + DNS logs</i>"] --> SIEM
RF["SPECTRE sensor<br/><i>ESP32-C5 WiFi · RFC 5424</i>"] --> SIEM
SIEM["<b>Wazuh SIEM + XDR</b><br/>decoders · normalisation · correlation"]
SIEM --> RULES["Detection logic<br/><i>Wazuh rulesets · MITRE ATT&CK mapping</i>"]
RULES --> SEV{"Triage"}
SEV -->|true positive| IR["Preserve · contain · eradicate<br/><i>evidence first, then isolate</i>"]
SEV -->|false positive| TUNE["Tune<br/><i>refine rule · allowlist</i>"]
SEV -->|benign true positive| DOC["Document & close<br/><i>so it is not re-investigated</i>"]
TUNE --> RULES
IR --> CASE["Case writeup<br/><i>NIST SP 800-61 · published</i>"]
classDef src fill:#0D1117,stroke:#455A64,color:#E6EDF3
classDef core fill:#161B22,stroke:#008F11,color:#E6EDF3
classDef out fill:#161B22,stroke:#0077B5,color:#E6EDF3
class EP,FWL,RF src
class SIEM,RULES,IR,TUNE,DOC core
class CASE out
| Project | What it proves | |
|---|---|---|
| 🛡️ | Security Analyst Portfolio | Detection engineering: IR playbooks · NIST writeups · ATT&CK-mapped detection logic |
| 🐍 | Automated Phish Extractor | Tier-1 SOC triage: .eml parsing, IOC defang, SPF/DMARC in 30s |
| 🛸 | Pelican Deepfield | Theme plugin for a game-server control panel. Shipping discipline: semver releases, tagged and changelogged |
| 🏠 | Home Network Lab | Defense-in-depth: VLAN segmentation · default-deny routing · centralized logging |
╔════════════════════════════════════════════════════════════╗
║ HARDENING SPECTRE supply chain + code scanning             ║
║           2026-09-12 -> 2026-09-14                         ║
╠════════════════════════════════════════════════════════════╣
║ PROBLEM   No code scanning configured at all · deps        ║
║           drifting until an advisory caught them           ║
║ FOUND     next 15.5.20 carried 10 advisories, two          ║
║           critical unauthenticated RCE:                    ║
║           GHSA-2xp9-vwfh-vxw4  image optimizer, AVIF       ║
║               WAS EXPLOITABLE · image route live until fix ║
║           CVE-2026-75604       windows-hosted server       ║
║               NOT APPLICABLE · Linux containers only       ║
║               patched anyway                               ║
║ FIXED     Bumped to 15.5.25 · used npm overrides to        ║
║           force patched versions of 4 transitive deps      ║
║           Disabled the image optimizer outright,           ║
║           dropping /_next/image from the attack surface    ║
╠════════════════════════════════════════════════════════════╣
║ CONTROLS  CodeQL: JS/TS · Python · Actions                 ║
║           Dependabot across five ecosystems                ║
║           Browser QA promoted to a required check          ║
║ STATUS    RESOLVED · 0 open advisories                     ║
╚════════════════════════════════════════════════════════════╝
╔════════════════════════════════════════════════════════════╗
║ OUTAGE    Wazuh SIEM full pipeline failure                 ║
║           2026-04-24                                       ║
╠════════════════════════════════════════════════════════════╣
║ PROBLEM   0 dashboard entries · all services active        ║
║ CAUSE     Admin hash mismatch · missing OpenSearch role    ║
║           Dashboard keystore overriding yml config         ║
║ FIXED     Auth chain repaired · roles created              ║
║           Keystore updated · auditd conflicts resolved     ║
╠════════════════════════════════════════════════════════════╣
║ RESULT    Log pipeline restored · alerting end to end      ║
║ HARDENED  CIS Ubuntu 24.04 L1    83.0% -> 88.9%            ║
║           USG Level 2 Server           90.98%              ║
║             435 of 471 rules · 36 open (34 med, 2 high)    ║
║ STATUS    RESOLVED                                         ║
╚════════════════════════════════════════════════════════════╝
B.S. Cybersecurity & Information Assurance · Western Governors University · expected 02/2027


USG = Ubuntu Security Guide, Level 2 Server profile. CIS = Center for Internet Security benchmark. Both scores are from audits run against my own hosts.
Detection & response


Network & systems


Build


Slo-Fi is a real-time audio engine that runs entirely in your browser. Nothing ever leaves the machine: no upload, no account, no server to breach. Cloudflare Workers serves static assets only; there is no server-side code.
Held to the same bar as the security work. 550+ assertions across five test layers, each layer floored independently in CI so a collapse in one cannot hide behind another's volume.

