Repository navigation
🐛 Stabilize device login and poll terminal authorization - #377
Merged
Merged
Conversation


Vizzly - Visual Test ResultsCLI Reporter - Waiting for buildNo builds received yet for this pull request. CLI TUI - 3 changes need review
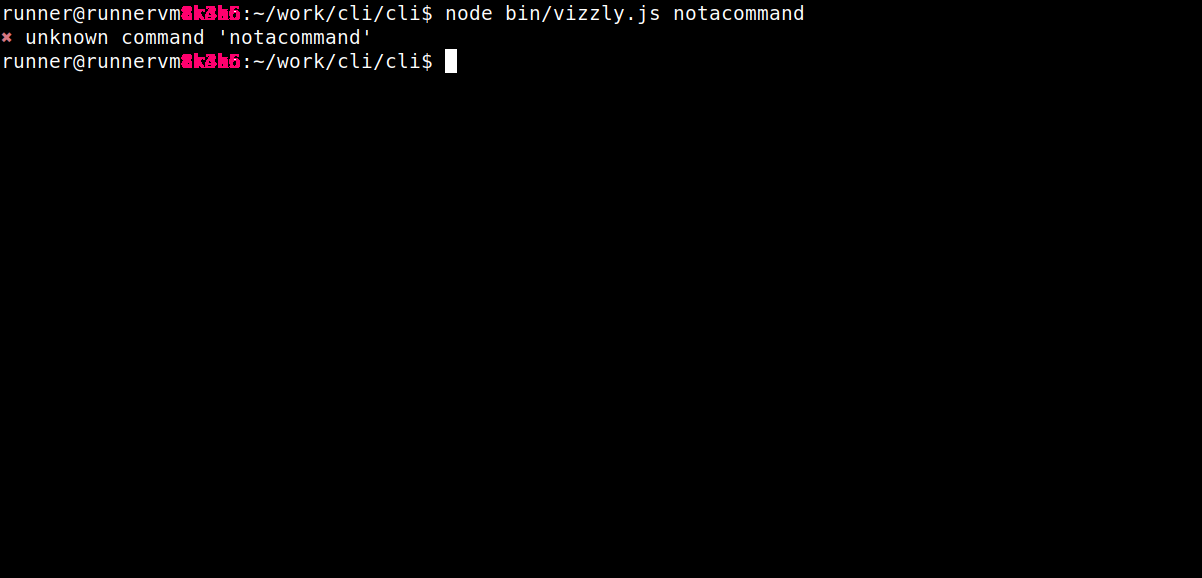
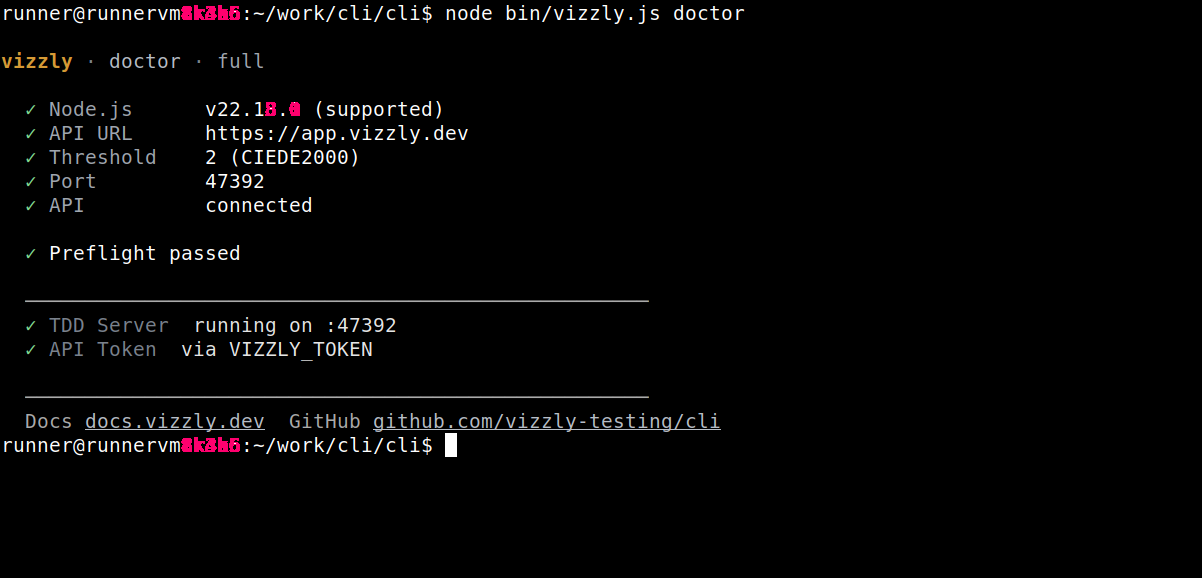
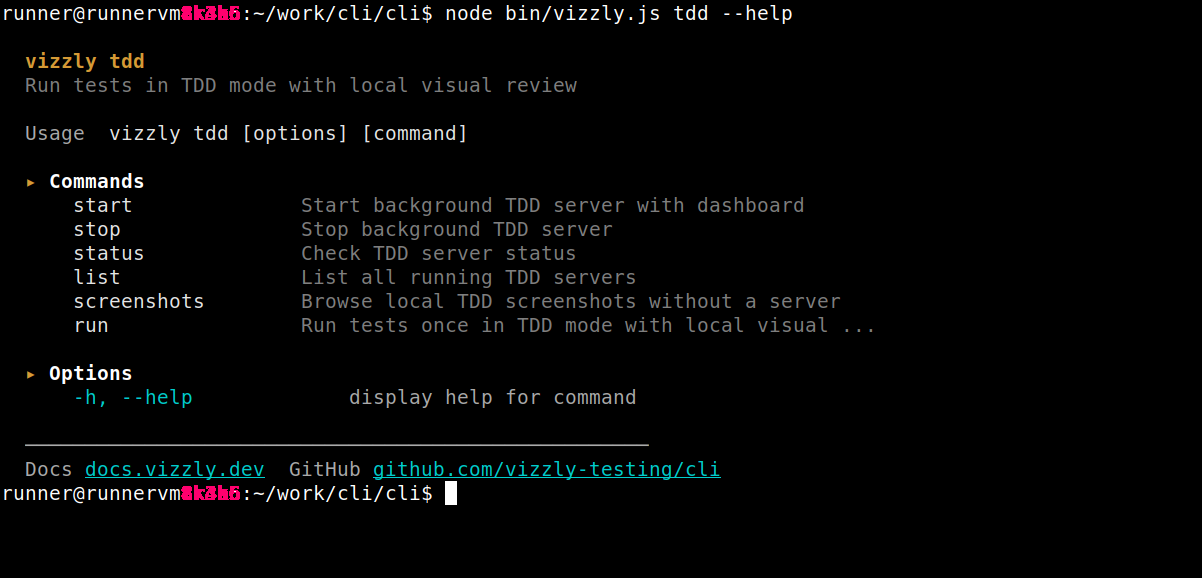
Meaningful diffs needing review (3)vizzly-invalid-command · 1202×578 · 0.2% diff vizzly-doctor · 1202×578 · 0.2% diff vizzly-tdd-help · 1202×578 · 0.2% diff
|

This file contains hidden or bidirectional Unicode text that may be interpreted or compiled differently than what appears below. To review, open the file in an editor that reveals hidden Unicode characters.
Learn more about bidirectional Unicode characters
Sign up for free
to join this conversation on GitHub.
Already have an account?
Sign in to comment
1 participant

Add this suggestion to a batch that can be applied as a single commit.This suggestion is invalid because no changes were made to the code.Suggestions cannot be applied while the pull request is closed.Suggestions cannot be applied while viewing a subset of changes.Only one suggestion per line can be applied in a batch.Add this suggestion to a batch that can be applied as a single commit.Applying suggestions on deleted lines is not supported.You must change the existing code in this line in order to create a valid suggestion.Outdated suggestions cannot be applied.This suggestion has been applied or marked resolved.Suggestions cannot be applied from pending reviews.Suggestions cannot be applied on multi-line comments.Suggestions cannot be applied while the pull request is queued to merge.Suggestion cannot be applied right now. Please check back later.
Dashboard sign-in can create a new device code on every render, preventing users from completing authorization. Start each flow from an explicit action, keep its code stable while pending, and ignore responses from dismissed attempts. Guard duplicate initiation and status checks, and make denial, expiry and retry behavior explicit.
Share device-response normalization and typed error handling across terminal login and the dashboard server. Preserve supported field aliases, throttling status and retry timing, keep credentials in Node, and authenticate server-side sign-out revocation.
Terminal login now checks automatically for up to two minutes. Interactive terminals show the next check and accept Enter for an early check; server cooldowns remain enforced. Closed stdin works for agents, stuck browser launchers fall back to the displayed URL, and successful login no longer shows a misleading access-token expiry countdown.
The complete Node suite passed with 2,002 tests and six existing skips. All 53 reporter browser workflows passed with five existing mobile skips; lint, formatting, build and published type checks passed. Real browser authorization, saved sessions, refresh, denial/retry, sign-out revocation and terminal countdown/Enter behavior were also verified. Regression coverage uses real CLI subprocesses, HTTP and disk persistence, controlled time, and browser race scenarios.
GitHub checks also passed on Node 22 and 24, including builds/types, reporter and TUI workflows, and every SDK E2E job. The inspected TUI visual differences are runner hostname and actual Node version. Nonblocking visual review requests remain for six new Vitest baselines and unchanged Ember/Ruby fixtures; those private build images require authenticated review.
Related to #376.